Ivanti Connect Secure zero-day chain (CVE-2026-104935) exploited for root
› Ivanti Connect Secure (ICS)
- started
- Oct 1, 2026
- closed
- ongoing
- CVEs
- 1
- sources
- 6
## summary
Volexity observed threat actor UTA0576 chaining an Ivanti Connect Secure authentication-bypass / RCE zero-day (CVE-2026-104935) with additional flaws from about Oct 1–3 2026 to get unauthenticated root on fully patched appliances, re-exploiting in memory without planting webshells. Ivanti patched CVE-2026-104935 on Oct 13; CISA added it to KEV. One privilege-escalation piece of the chain was still being fixed at disclosure.
severity: High (CVSS ~8.6 reported in secondary sources); actively exploited / CISA KEV
## cve ids[1]
## affected
- 22.8R2.4 and earlier; 25.1.2.2 and earlier; 25.1.1.1 and earlier (per Ivanti / BleepingComputer)
## fixed in
- Ivanti October 2026 Security Update for CVE-2026-104935 (see Ivanti advisory)
## updates by day[4]
▸Oct 13, 2026
permalink ↗Ivanti discloses and patches CVE-2026-104935; Volexity publishes.
CISA KEV listing; federal patching deadline reported as Oct 16.
▸Oct 3, 2026
permalink ↗Volexity sees UTA0576 chaining for unauth root.
▸Oct 1, 2026
permalink ↗Defused reports first signs of exploitation.
## advisories[3]
## posts[3]

welcome.cgi → root. Ivanti Connect Secure CVE-2026-104935. Zero-day. ITW. KEV. UTA0576 chain (Volexity): • public welcome.cgi + X-DSCGI-PATH → hit protected wu.cgi unauth • zip-upload race → execute the Perl before delete • dsinvoked + in-memory lib patch → root • ICT

🚨 IVANTI CONNECT SECURE ZERO-DAY CHAIN EXPLOITED TO STEAL CREDENTIALS (CVE-2026-104935) Ivanti disclosed a new Connect Secure (ICS) VPN flaw on Oct 13, 2026 and says it is aware of limited exploitation in the wild. CISA added it to the KEV catalog the same day. Volexity t.co/o24PhxS5jy
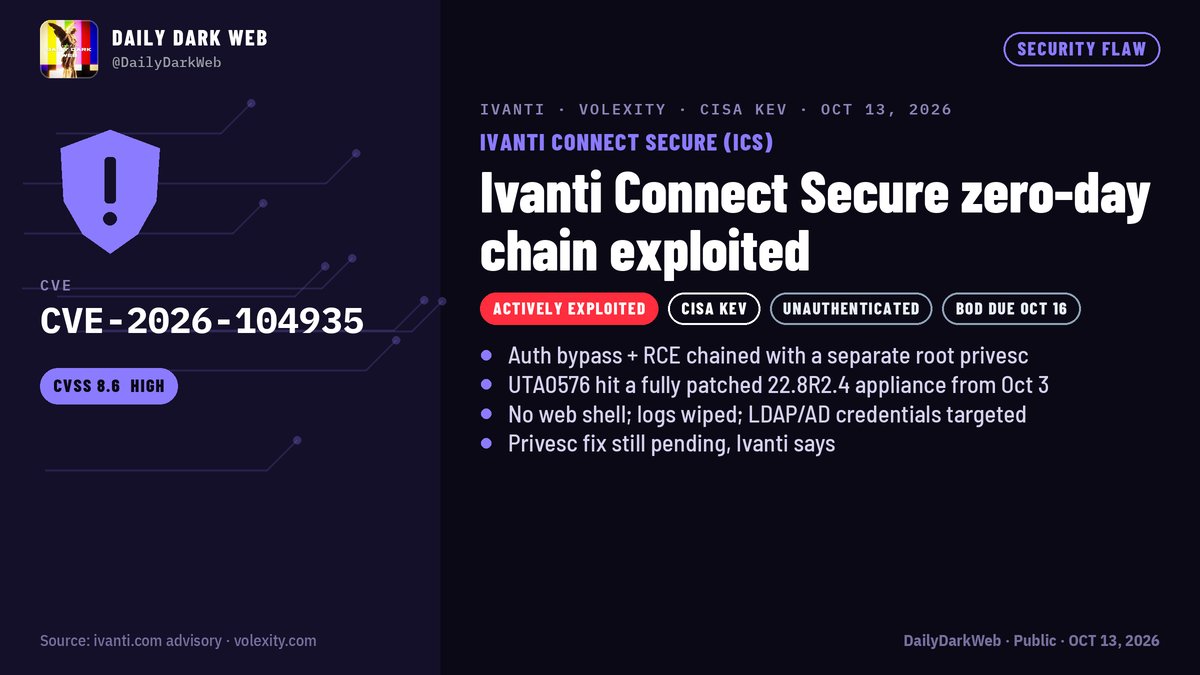

UTA0576 chained an Ivanti Connect Secure zero-day, CVE-2026-104935, with a root exploit to steal AD credentials. Patch now and check memory. #Ivanti #ZeroDay #CVE2026104935 #UTA0576 #Volexity #VPN #ActiveDirectory #Cybersecurity t.co/Yb0bCtOh60
## notes & caveats
Exact fixed version strings should be taken from Ivanti’s advisory. Volexity reported a still-unpatched privilege-escalation piece in the chain at disclosure — patchStatus partial / lifecycle live.

