Skip to content

Get notified

Get an email when a new major security incident drops. No spam, unsubscribe any time.

Only used for pwn.watch incident emails. Protected by Cloudflare Turnstile.

Zero-day

Security incidents tagged Zero-day. Newest first.

Incidents
47
Live
3
Patched
44
Days without an incident
0
Longest quiet run: 105 days (Jan 9–Apr 23)
  • ClosedHighPatched

    Windows Shell Mark-of-the-Web bypass zero-day (CVE-2026-96951)

    Microsoft’s October 13 2026 Patch Tuesday fixed an actively exploited Windows Shell security-feature bypass, CVE-2026-96951, that can evade Mark of the Web protections (command-injection style neutralization flaw). CISA added it to KEV. Two other publicly disclosed zero-days (.NET Framework WDAC bypass CVE-2026-108398 and MessagePack-CSharp DoS CVE-2026-92707) shipped in the same release.

    Microsoft Windows Shell (and related Oct Patch Tuesday components)Closed Oct 13, 2026

  • LiveHighPartly patched

    Ivanti Connect Secure zero-day chain (CVE-2026-104935) exploited for root

    Volexity observed threat actor UTA0576 chaining an Ivanti Connect Secure authentication-bypass / RCE zero-day (CVE-2026-104935) with additional flaws from about Oct 1–3 2026 to get unauthenticated root on fully patched appliances, re-exploiting in memory without planting webshells. Ivanti patched CVE-2026-104935 on Oct 13; CISA added it to KEV. One privilege-escalation piece of the chain was still being fixed at disclosure.

    Ivanti Connect Secure (ICS)Since Oct 1, 2026

  • LiveCriticalPatched

    FortiMail unauthenticated file-write zero-day CVE-2026-104286

    Fortinet FortiMail CVE-2026-104286 (CVSS 9.8) is an unauthenticated arbitrary file write via path traversal / null-byte issues in Identity-Based Encryption web flows. CISA confirmed active exploitation and ordered federal mitigation; Fortinet published FG-IR-26-175 with patches and interim mitigations (disable IBE / restrict admin/webmail).

    Fortinet FortiMailSince Sep 30, 2026

  • HighApple CoreGraphics zero-day CVE-2026-86950

    Apple iOS, iPadOS, macOS (CoreGraphics) Patched

    Apple patched CVE-2026-86950, an out-of-bounds write in CoreGraphics that may lead to arbitrary code execution, and indicated it may have been exploited in a sophisticated targeted attack against earlier iOS versions. Fixed in iOS/iPadOS 26.7.1 and corresponding macOS updates. CISA added to KEV Sept 29.

    Open incident →CVE-2026-86950
Show 43 older incidents

September 2026 2

  • HighChrome zero-day CVE-2026-87491 (V8 OOB write)

    Google Chrome / Chromium V8 Patched

    September 9 2026 Chrome 153 patched CVE-2026-87491, a V8 out-of-bounds write Google said was exploited in the wild — the seventh Chrome zero-day of 2026. Fixed in 153.0.8010.36/.37. CISA KEV listed.

    Open incident →CVE-2026-87491
  • HighChrome zero-day CVE-2026-85046 (V8 type confusion)

    Google Chrome / Chromium V8 Patched

    September 4 2026 Chrome update patched CVE-2026-85046, a V8 type confusion zero-day Google said was exploited in the wild. Fixed in Chrome 152.0.7977.82/.83. Later added to CISA KEV.

    Open incident →CVE-2026-85046

August 2026 1

  • LiveCriticalPartly patched

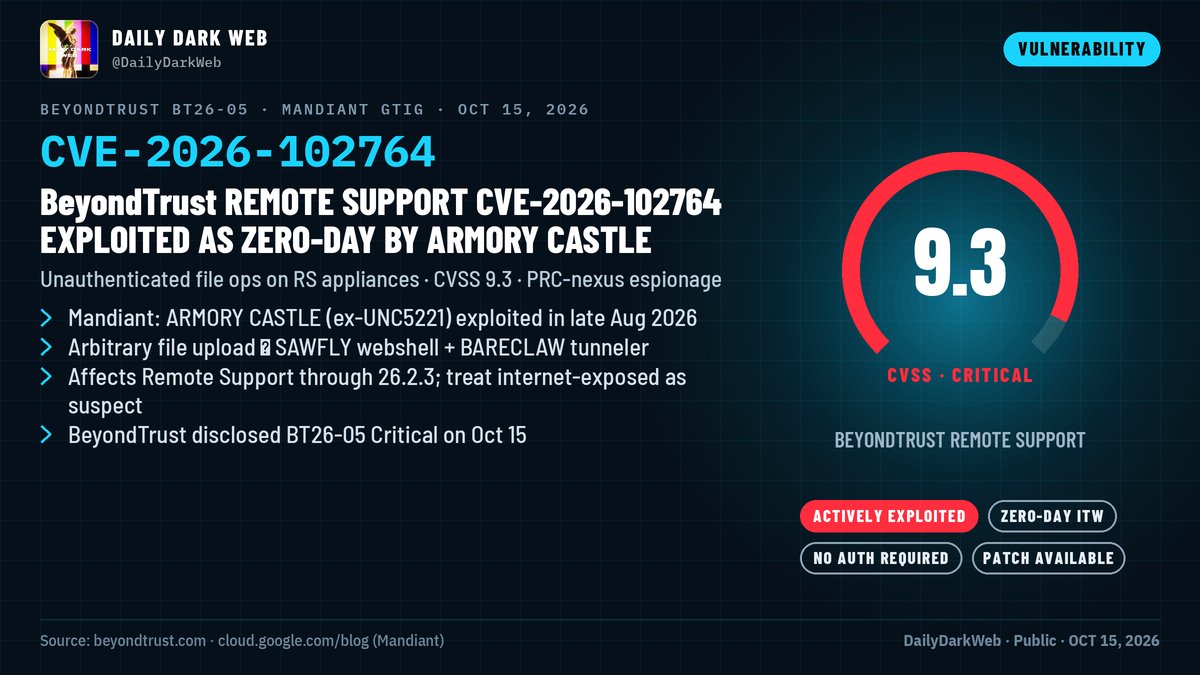
    BeyondTrust Remote Support zero-day CVE-2026-102764 (ARMORY CASTLE)

    China-nexus actor ARMORY CASTLE (ex-UNC5221) exploited CVE-2026-102764, a critical unauthenticated file-operations flaw in BeyondTrust Remote Support, as a zero-day from late August 2026. BeyondTrust issued BT26-05-RS; SaaS was auto-patched by Oct 9; CISA added the CVE to KEV on Oct 16. Self-hosted appliances need the patch plus forensics — patching alone does not clear existing footholds (SAWFLY / BARECLAW).

    BeyondTrust Remote Support (formerly Bomgar)Since Aug 29, 2026

June 2026 1

  • HighChrome zero-day CVE-2026-11645 (V8 OOB)

    Google Chrome / Chromium V8 Patched

    June 2026 Chrome emergency update patched CVE-2026-11645, an out-of-bounds read/write in V8 exploited in the wild (fifth Chrome zero-day of 2026 at the time). Stable builds 149.0.7827.102/.103.

    Open incident →CVE-2026-11645

April 2026 1

  • HighChrome zero-day CVE-2026-5281 (Dawn / WebGPU UAF)

    Google Chrome / Chromium Dawn Patched

    April 2026 Chrome patch for CVE-2026-5281, a use-after-free in Dawn (WebGPU), actively exploited in the wild.

    Open incident →CVE-2026-5281

March 2026 1

  • HighChrome zero-days CVE-2026-3909 (Skia) and CVE-2026-3910 (V8)

    Google Chrome / Chromium Patched

    March 2026 Chrome updates fixed two actively exploited zero-days: CVE-2026-3909 (out-of-bounds write in Skia) and CVE-2026-3910 (inappropriate implementation in V8).

    Open incident →CVE-2026-3909 · CVE-2026-3910

February 2026 4

  • HighChrome zero-day CVE-2026-2441 (CSS use-after-free)

    Google Chrome / Chromium Patched

    First actively exploited Chrome zero-day of 2026. Google patched CVE-2026-2441, a high-severity use-after-free in CSS (CSSFontFeatureValuesMap), in mid-February Chrome 145 updates. Google stated an exploit existed in the wild.

    Open incident →CVE-2026-2441
  • CriticalCisco Catalyst SD-WAN zero-day campaign (CISA emergency directive)

    Cisco Catalyst SD-WAN Manager / controllers Patched

    In February 2026 CISA issued an emergency directive after exploitation of critical authentication-bypass and related flaws in Cisco Catalyst SD-WAN Manager/controllers. Cisco Talos said related activity dated back years; unauthenticated attackers could gain administrative privileges on exposed controllers.

  • CriticalEuropean Commission & Dutch authorities hit via Ivanti EPMM zero-days

    Ivanti EPMM deployments (EU institutions) Patched

    February 2026: European Commission and Dutch DPA/Judicial Council confirmed breaches through critical Ivanti Endpoint Manager Mobile zero-days. Dutch incident exposed work contact data; Commission said it contained its breach within nine hours.

    Open incident →CVE-2026-1340
  • UnratedUNC3886 breaches Singapore telecom providers (CYBER GUARDIAN)

    Singapore major telecom providers Partly patched

    In February 2026 Singapore’s CSA revealed China-linked UNC3886 had breached all four major telecom providers in a months-long espionage campaign using zero-days and rootkits. Singapore ran operation CYBER GUARDIAN to evict the actors.

December 2025 1

  • ClosedCriticalPatched

    React2Shell: CVSS 10 unauthenticated RCE in React Server Components and Next.js

    A flaw in how React Server Components deserialize Flight payloads let an unauthenticated request run code on the server. Next.js App Router apps were affected by default. China-nexus groups including Earth Lamia and Jackpot Panda exploited it within hours of disclosure. CVE-2025-66478 (the Next.js id) was rejected as a duplicate.

    React Server Components (react-server-dom-*), Next.jsClosed Dec 12, 2025

September 2025 1

  • ClosedCriticalPatched

    Cl0p extortion campaign via Oracle E-Business Suite zero-day (CVE-2025-61882)

    Cl0p-branded extortion emails reached executives from September 29, 2025, claiming theft of Oracle E-Business Suite data. Mandiant tied the campaign to exploitation of an unauthenticated RCE in EBS (SyncServlet), patched as CVE-2025-61882 for EBS 12.2.3 to 12.2.14. A separate July UiServlet SSRF campaign was later tracked as CVE-2025-61884.

    Oracle E-Business SuiteClosed Oct 20, 2025

July 2025 1

  • ClosedCriticalPatched

    ToolShell: mass exploitation of on-prem SharePoint (CVE-2025-53770, CVE-2025-49704, CVE-2025-49706)

    Unauthenticated RCE chain against on-premises SharePoint Server, mass-exploited from July 18, 2025. Microsoft observed Linen Typhoon, Violet Typhoon and Storm-2603 exploiting it; Storm-2603 deployed Warlock ransomware. Patching alone is not enough: rotate ASP.NET machine keys and restart IIS. SharePoint Online was not affected.

    Microsoft SharePoint Server (on-premises)Closed Jul 22, 2025

June 2025 1

  • ClosedCriticalPatched

    CitrixBleed 2: NetScaler memory leak exploited to hijack sessions

    An out-of-bounds read in NetScaler ADC and Gateway leaked memory, including session tokens, to unauthenticated attackers. GreyNoise saw exploitation from June 23, before public PoCs on July 4. After patching, admins had to kill all active ICA, PCoIP, RDP, AAA and LB sessions.

    Citrix NetScaler ADC and GatewayClosed Jul 10, 2025

April 2025 1

  • CriticalSAP NetWeaver Visual Composer zero-day: unauthenticated webshell uploads (CVE-2025-31324)

    SAP NetWeaver Visual Composer Patched

    A CVSS 10 missing-authorization flaw in the NetWeaver Visual Composer Metadata Uploader let anyone POST JSP webshells to /developmentserver/metadatauploader. ReliaQuest found it while investigating compromises; SAP shipped an emergency fix on April 24, 2025.

    Open incident →CVE-2025-31324

January 2025 1

  • CriticalIvanti Connect Secure zero-day exploited since mid-December 2024 (CVE-2025-0282)

    Ivanti Connect Secure, Policy Secure, ZTA Gateways Patched

    An unauthenticated stack buffer overflow in Ivanti Connect Secure allowed remote code execution. Mandiant saw zero-day exploitation from mid-December 2024 and SPAWN-family malware (SPAWNANT, SPAWNMOLE, SPAWNSNAIL). CISA advised factory-resetting compromised appliances before restoring them on 22.7R2.5 or later.

    Open incident →CVE-2025-0282

December 2024 1

  • CriticalCleo file transfer zero-days exploited by Clop for data theft

    Cleo Multiple Products Patched

    Two unauthenticated file-write bugs in Cleo Harmony, VLTrader and LexiCom managed file transfer software (CVE-2024-50623 and CVE-2024-55956) were mass-exploited in December 2024 to plant a Java backdoor and steal data. Huntress saw exploitation from 2024-12-03 against systems already patched to 5.8.0.21; Cleo shipped 5.8.0.24 for the second bug. The Clop ransomware gang claimed the attacks. Added to the CISA KEV catalog on 2024-12-13, 2024-12-17. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-50623 · CVE-2024-55956

November 2024 2

  • CriticalPalo Alto PAN-OS management interface auth bypass + privilege escalation

    Palo Alto Networks PAN-OS Patched

    CVE-2024-0012: Palo Alto Networks PAN-OS contains an authentication bypass vulnerability in the web-based management interface for several PAN-OS products, including firewalls and VPN concentrators. CVE-2024-9474: Palo Alto Networks PAN-OS contains an OS command injection vulnerability that allows for privilege escalation through the web-based management interface for several PAN products, including firewalls and VPN concentrators. Added to the CISA KEV catalog on 2024-11-18. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-0012 · CVE-2024-9474
  • HighMicrosoft November 2024: 2 actively exploited zero-days

    Microsoft Windows Patched

    CVE-2024-43451: Microsoft Windows contains an NTLMv2 hash spoofing vulnerability that could result in disclosing a user's NTLMv2 hash to an attacker via a file open operation. The attacker could then leverage this hash to impersonate that user. CVE-2024-49039: Microsoft Windows Task Scheduler contains a privilege escalation vulnerability that can allow an attacker-provided, local application to escalate privileges outside of its AppContainer, and access privileged RPC functions. Added to the CISA KEV catalog on 2024-11-12. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-43451 · CVE-2024-49039

October 2024 2

  • CriticalFortiManager 'FortiJump' missing authentication zero-day (CVE-2024-47575)

    Fortinet FortiManager Patched

    Fortinet FortiManager contains a missing authentication vulnerability in the fgfmd daemon that allows a remote, unauthenticated attacker to execute arbitrary code or commands via specially crafted requests. Added to the CISA KEV catalog on 2024-10-23.

    Open incident →CVE-2024-47575
  • HighMicrosoft October 2024: 2 actively exploited zero-days

    Microsoft Windows Patched

    CVE-2024-43572: Microsoft Windows Management Console contains unspecified vulnerability that allows for remote code execution. CVE-2024-43573: Microsoft Windows MSHTML Platform contains an unspecified spoofing vulnerability which can lead to a loss of confidentiality. Added to the CISA KEV catalog on 2024-10-08.

    Open incident →CVE-2024-43572 · CVE-2024-43573

September 2024 2

  • CriticalIvanti Cloud Services Appliance zero-days chained by a suspected nation-state actor

    Ivanti Cloud Services Appliance / Cloud Services Appliance (CSA) Patched

    Four Ivanti Cloud Services Appliance (CSA) bugs were exploited in 2024: a command injection (CVE-2024-8190), a path traversal admin bypass (CVE-2024-8963), and later a SQL injection and another command injection (CVE-2024-9379, CVE-2024-9380). FortiGuard Incident Response found a suspected nation-state actor chaining them. CSA 4.6 was end-of-life; Ivanti urged upgrading to CSA 5.0. Added to the CISA KEV catalog on 2024-09-13, 2024-09-19, 2024-10-09.

    Open incident →CVE-2024-8190 · CVE-2024-8963 · CVE-2024-9379 +1
  • HighMicrosoft September 2024: 3 actively exploited zero-days

    Microsoft Publisher, Windows Patched

    CVE-2024-38014: Microsoft Windows Installer contains an improper privilege management vulnerability that could allow an attacker to gain SYSTEM privileges. CVE-2024-38217: Microsoft Windows Mark of the Web (MOTW) contains a protection mechanism failure vulnerability that allows an attacker to bypass MOTW-based defenses. This can result in a limited loss of integrity and availability of security features such as Protected View in Microsoft Office, which rely on MOTW tagging. CVE-2024-38226: Microsoft Publisher contains a protection mechanism failure vulnerability that allows attacker to bypass Office macro policies used to block untrusted or malicious files. Added to the CISA KEV catalog on 2024-09-10.

    Open incident →CVE-2024-38014 · CVE-2024-38217 · CVE-2024-38226

August 2024 1

  • HighMicrosoft August 2024: 6 actively exploited zero-days

    Microsoft Project, Windows Patched

    CVE-2024-38106: Microsoft Windows Kernel contains an unspecified vulnerability that allows for privilege escalation, enabling a local attacker to gain SYSTEM privileges. Successful exploitation of this vulnerability requires an attacker to win a race condition. CVE-2024-38107: Microsoft Windows Power Dependency Coordinator contains an unspecified vulnerability that allows for privilege escalation, enabling a local attacker to obtain SYSTEM privileges. CVE-2024-38178: Microsoft Windows Scripting Engine contains a memory corruption vulnerability that allows unauthenticated attacker to initiate remote code execution via a specially crafted URL. CVE-2024-38189: Microsoft Project contains an unspecified vulnerability that allows for remote code execution via a malicious file. CVE-2024-38193: Microsoft Windows Ancillary Function Driver for WinSock contains an unspecified vulnerability that allows for privilege escalation, enabling a local attacker to gain SYSTEM privileges. CVE-2024-38213: Microsoft Windows SmartScreen contains a security feature bypass vulnerability that allows an attacker to bypass the SmartScreen user experience via a malicious file. Added to the CISA KEV catalog on 2024-08-13.

    Open incident →CVE-2024-38106 · CVE-2024-38107 · CVE-2024-38178 +3

July 2024 1

  • HighMicrosoft July 2024: 2 actively exploited zero-days

    Microsoft Windows Patched

    CVE-2024-38080: Microsoft Windows Hyper-V contains a privilege escalation vulnerability that allows a local attacker with user permissions to gain SYSTEM privileges. CVE-2024-38112: Microsoft Windows MSHTML Platform contains a spoofing vulnerability that has a high impact to confidentiality, integrity, and availability. Added to the CISA KEV catalog on 2024-07-09.

    Open incident →CVE-2024-38080 · CVE-2024-38112

May 2024 1

  • HighMicrosoft May 2024: 2 actively exploited zero-days

    Microsoft DWM Core Library, Windows Patched

    CVE-2024-30040: Microsoft Windows MSHTML Platform contains an unspecified vulnerability that allows for a security feature bypass. CVE-2024-30051: Microsoft DWM Core Library contains a privilege escalation vulnerability that allows an attacker to gain SYSTEM privileges. Added to the CISA KEV catalog on 2024-05-14. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-30040 · CVE-2024-30051

April 2024 2

  • HighCisco ASA/FTD zero-days used in the ArcaneDoor espionage campaign

    Cisco Adaptive Security Appliance (ASA) and Firepower Threat Defense (FTD) Patched

    Cisco Talos disclosed ArcaneDoor, a state-sponsored campaign against perimeter devices that exploited two Cisco Adaptive Security Appliance and Firepower Threat Defense zero-days: a denial of service (CVE-2024-20353) and a persistent local code execution bug (CVE-2024-20359), used to plant the Line Dancer and Line Runner implants. Added to the CISA KEV catalog on 2024-04-24.

    Open incident →CVE-2024-20353 · CVE-2024-20359
  • CriticalPalo Alto PAN-OS GlobalProtect zero-day (CVE-2024-3400)

    Palo Alto Networks PAN-OS Patched

    A command injection in the GlobalProtect feature of PAN-OS let unauthenticated attackers run code as root on Palo Alto firewalls (CVSS 10). Volexity caught an actor it tracks as UTA0218, assessed as likely state-backed, exploiting it as a zero-day, and Palo Alto's Unit 42 tracked the activity as Operation MidnightEclipse. Hotfixes shipped from mid-April 2024. Added to the CISA KEV catalog on 2024-04-12. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-3400

February 2024 1

  • HighMicrosoft February 2024: 2 actively exploited zero-days

    Microsoft Windows Patched

    CVE-2024-21351: Microsoft Windows SmartScreen contains a security feature bypass vulnerability that allows an attacker to bypass the SmartScreen user experience and inject code to potentially gain code execution, which could lead to some data exposure, lack of system availability, or both. CVE-2024-21412: Microsoft Windows Internet Shortcut Files contains an unspecified vulnerability that allows for a security feature bypass. Added to the CISA KEV catalog on 2024-02-13. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2024-21351 · CVE-2024-21412

January 2024 1

  • CriticalIvanti Connect Secure zero-days chained for mass VPN compromise

    Ivanti Connect Secure and Policy Secure / Connect Secure, Policy Secure, and Neurons Patched

    Two Ivanti Connect Secure and Policy Secure zero-days, an authentication bypass (CVE-2023-46805) and a command injection (CVE-2024-21887), were chained for unauthenticated remote code execution on internet-facing VPN gateways. Volexity found them in the wild in December 2023 and disclosed them on 2024-01-10. A third bug, an SSRF in the SAML component (CVE-2024-21893), was exploited later in January. CISA issued Emergency Directive 24-01 and then ordered federal agencies to disconnect all Ivanti Connect Secure and Policy Secure appliances. Added to the CISA KEV catalog on 2024-01-10, 2024-01-31. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2023-46805 · CVE-2024-21887 · CVE-2024-21893

October 2023 2

  • ClosedCriticalPatched

    Citrix Bleed: NetScaler session token leak (CVE-2023-4966)

    A memory leak in NetScaler ADC and Gateway let attackers read session tokens and hijack logged-in sessions, bypassing passwords and MFA. It was exploited as a zero-day from late August 2023, then widely by LockBit affiliates. Victims included Xfinity (35.9M users).

    Citrix NetScaler ADC and NetScaler GatewayClosed Nov 21, 2023

  • CriticalConfluence Data Center/Server zero-day lets attackers create admins (CVE-2023-22515)

    Atlassian Confluence Data Center and Server Patched

    A broken access control bug in publicly reachable Confluence Data Center and Server let outside attackers create Confluence administrator accounts. It was exploited as a zero-day, and Microsoft attributed it to the China-nexus Storm-0062. Atlassian Cloud was not affected.

    Open incident →CVE-2023-22515

September 2023 3

  • ClosedCriticalPatched

    Cisco IOS XE web UI zero-days: implants on tens of thousands of devices

    Attackers chained two zero-days in the Cisco IOS XE web UI. CVE-2023-20198 let them create a privilege-15 account, and CVE-2023-20273 let them write a root-level implant. Internet scans soon found implants on tens of thousands of switches and routers.

    Cisco IOS XE Software (web UI)Closed Oct 23, 2023

  • Highlibwebp heap overflow exploited in the wild (CVE-2023-4863)

    libwebp (Google Chrome and everything that bundles libwebp) Patched

    A heap overflow in libwebp's lossless decoder, found by Apple SEAR and Citizen Lab after the BLASTPASS iPhone exploit, was exploited in the wild. Because libwebp is everywhere, browsers, Electron apps and image libraries that bundle it all had to ship updates.

    Open incident →CVE-2023-4863
  • HighBLASTPASS: NSO zero-click iPhone exploit chain (CVE-2023-41064, CVE-2023-41061)

    Apple iOS, iPadOS, macOS and watchOS Patched

    Citizen Lab caught BLASTPASS, a zero-click iMessage exploit chain that delivered NSO Group's Pegasus through malicious PassKit attachments carrying images. Apple fixed the ImageIO and Wallet bugs in emergency updates the same day.

    Open incident →CVE-2023-41064 · CVE-2023-41061

August 2023 1

  • HighWinRAR zero-day used against traders, then state hackers (CVE-2023-38831)

    RARLAB WinRAR Patched

    WinRAR before 6.23 would run hidden code when a user opened what looked like a harmless file inside a ZIP. Group-IB found it exploited since April 2023 to target traders. After the fix, Google TAG saw Russian and Chinese government-backed groups pile on.

    Open incident →CVE-2023-38831

July 2023 2

  • CriticalIvanti EPMM zero-days used to breach 12 Norwegian ministries

    Ivanti Endpoint Manager Mobile (EPMM / MobileIron Core) Patched

    APT actors exploited an unauthenticated API access bug in Ivanti Endpoint Manager Mobile (formerly MobileIron Core) as a zero-day from at least April 2023. They used it to break into the shared IT platform of 12 Norwegian government ministries, possibly chaining it with a file-write bug (CVE-2023-35081).

    Open incident →CVE-2023-35078 · CVE-2023-35081
  • CriticalNetScaler ADC/Gateway unauthenticated RCE (CVE-2023-3519)

    Citrix NetScaler ADC and NetScaler Gateway Patched

    An unauthenticated code injection in NetScaler ADC and Gateway was exploited as a zero-day to plant webshells, including on a US critical infrastructure organisation in June 2023. Citrix patched it on July 18, 2023.

    Open incident →CVE-2023-3519

June 2023 1

  • HighOperation Triangulation: zero-click iMessage spyware on Kaspersky's iPhones

    Apple iOS (and other Apple OSes sharing the bugs) Patched

    Kaspersky found a years-long zero-click iMessage campaign on its own staff's iPhones. The chain used several Apple zero-days, including a bypass of hardware memory protections through undocumented MMIO registers (CVE-2023-38606), which was revealed at 37C3 in December 2023.

    Open incident →CVE-2023-32434 · CVE-2023-32435 · CVE-2023-38606

May 2023 2

  • ClosedCriticalPatched

    MOVEit Transfer zero-day: Cl0p mass data theft

    Cl0p (Lace Tempest) exploited an unauthenticated SQL injection in Progress MOVEit Transfer as a zero-day, stealing files from thousands of organisations through their managed file transfer servers. Progress shipped three rounds of fixes in June 2023 as more SQL injection bugs were found.

    Progress MOVEit TransferClosed Jun 16, 2023

  • ClosedCriticalPatched

    Barracuda Email Security Gateway zero-day (CVE-2023-2868)

    A command injection in how Barracuda ESG appliances scan .tar attachments was exploited since October 2022 by China-nexus UNC4841 to backdoor appliances. Barracuda later told customers to replace compromised appliances outright, even after patching.

    Barracuda Email Security Gateway (appliance)Closed Jun 15, 2023

March 2023 1

  • CriticalOutlook zero-click NTLM hash leak used by Russian state hackers (CVE-2023-23397)

    Microsoft Outlook for Windows Patched

    A crafted Outlook reminder with a UNC path made Outlook for Windows send the user's NTLM hash to an attacker's server without any click. Microsoft said a Russia-based actor (APT28) used it against European government, transport, energy and military targets.

    Open incident →CVE-2023-23397

February 2023 1

  • HighFortra GoAnywhere MFT zero-day: Cl0p claims 130 victims

    Fortra GoAnywhere MFT Patched

    A pre-auth deserialization/command injection in the GoAnywhere MFT admin console's License Response Servlet was exploited as a zero-day. The Cl0p gang said it stole data from more than 130 organisations, a rehearsal for the later MOVEit campaign.

    Open incident →CVE-2023-0669

15 Zero-day incidents in the last 12 months

Critical 4 · High 3 · Med 2 · Low 1 · Update ½LessMore

Posts 12

+6 more on the incident pages above.