Skip to content

Get notified

Get an email when a new major security incident drops. No spam, unsubscribe any time.

Only used for pwn.watch incident emails. Protected by Cloudflare Turnstile.

Ivanti

Security incidents tagged Ivanti. Newest first.

7 Ivanti incidents in the last 12 months

Critical 4 · High 3 · Med 2 · Low 1 · Update ½LessMore
Incidents
19
Live
1
Patched
18
Days without an incident
0
Longest quiet run: 254 days (May 20–Jan 28)
  • LiveHighPartly patched

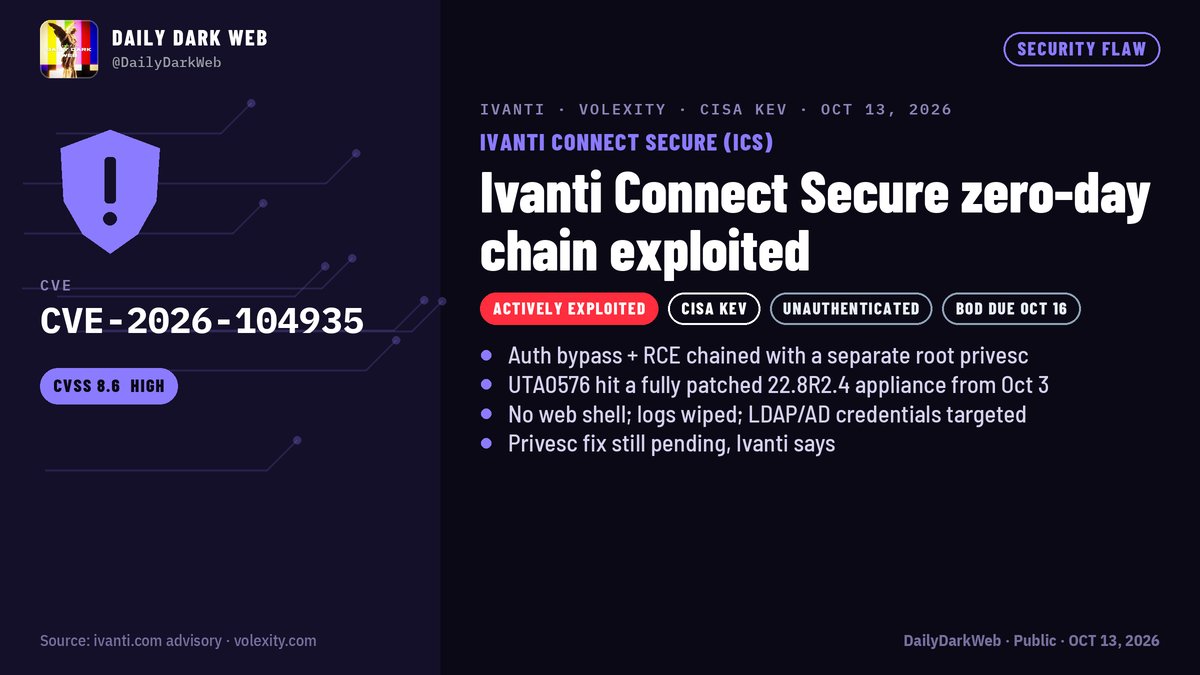
    Ivanti Connect Secure zero-day chain (CVE-2026-104935) exploited for root

    Volexity observed threat actor UTA0576 chaining an Ivanti Connect Secure authentication-bypass / RCE zero-day (CVE-2026-104935) with additional flaws from about Oct 1–3 2026 to get unauthenticated root on fully patched appliances, re-exploiting in memory without planting webshells. Ivanti patched CVE-2026-104935 on Oct 13; CISA added it to KEV. One privilege-escalation piece of the chain was still being fixed at disclosure.

    Ivanti Connect Secure (ICS)Since Oct 1, 2026

Show 18 older incidents

June 2026 1

  • PatchedIvanti Sentry: Ivanti Sentry OS Command Injection Vulnerability

    Ivanti Sentry

    Ivanti Sentry (formerly known as MobileIron Sentry) contains an OS command injection vulnerability which could allow a remote unauthenticated user to achieve root-level remote code execution. This vulnerability can be successfully exploited in cases where the Sentry appliance is in an unmanaged state with its endpoints externally reachable. The use of mTLS with EPMM or restricted HTTPS access through Neurons for MDM makes interfaces inaccessible to external actors. Added to CISA KEV on 2026-06-11.

    Open incident →CVE-2026-10520

May 2026 1

  • PatchedIvanti Endpoint Manager Mobile (EPMM): Ivanti Endpoint Manager Mobile (EPMM) Improper Input Validation Vulnerability

    Ivanti Endpoint Manager Mobile (EPMM)

    Ivanti Endpoint Manager Mobile (EPMM) contains an improper input validation vulnerability that allows a remotely authenticated user with administrative access to achieve remote code execution. Added to CISA KEV on 2026-05-07.

    Open incident →CVE-2026-6973

March 2026 1

  • PatchedIvanti Endpoint Manager (EPM): Ivanti Endpoint Manager (EPM) Authentication Bypass Vulnerability

    Ivanti Endpoint Manager (EPM)

    Ivanti Endpoint Manager (EPM) contains an authentication bypass using an alternate path or channel vulnerability that could allow a remote unauthenticated attacker to leak specific stored credential data. Added to CISA KEV on 2026-03-09.

    Open incident →CVE-2026-1603

February 2026 1

  • PatchedEuropean Commission & Dutch authorities hit via Ivanti EPMM zero-days

    Ivanti EPMM deployments (EU institutions)

    February 2026: European Commission and Dutch DPA/Judicial Council confirmed breaches through critical Ivanti Endpoint Manager Mobile zero-days. Dutch incident exposed work contact data; Commission said it contained its breach within nine hours.

    Open incident →CVE-2026-1340

January 2026 2

  • PatchedIvanti EPMM code injection CVE-2026-1340 exploited

    Ivanti Endpoint Manager Mobile (EPMM)

    Ivanti Endpoint Manager Mobile (EPMM) CVE-2026-1340 — unauthenticated RCE via code injection — was exploited in limited attacks disclosed late January 2026. CISA later ordered federal agencies to patch within days in April when adding/prioritizing the KEV entry.

    Open incident →CVE-2026-1340
  • PatchedIvanti Endpoint Manager Mobile (EPMM): Ivanti Endpoint Manager Mobile (EPMM) Code Injection Vulnerability

    Ivanti Endpoint Manager Mobile (EPMM)

    Ivanti Endpoint Manager Mobile (EPMM) contains a code injection vulnerability that could allow attackers to achieve unauthenticated remote code execution. Added to CISA KEV on 2026-01-29.

    Open incident →CVE-2026-1281

May 2025 1

  • PatchedIvanti Endpoint Manager Mobile (EPMM): 2 exploited vulnerabilities (CVE-2025-4427, CVE-2025-4428)

    Ivanti Endpoint Manager Mobile (EPMM)

    CVE-2025-4427: Ivanti Endpoint Manager Mobile (EPMM) contains an authentication bypass vulnerability in the API component that allows an attacker to access protected resources without proper credentials via crafted API requests. This vulnerability results from an insecure implementation of the Spring Framework open-source library. CVE-2025-4428: Ivanti Endpoint Manager Mobile (EPMM) contains a code injection vulnerability in the API component that allows an authenticated attacker to remotely execute arbitrary code via crafted API requests. This vulnerability results from an insecure implementation of the Hibernate Validator open-source library, as represented by CVE-2025-35036. Added to CISA KEV on 2025-05-19.

    Open incident →CVE-2025-4427 · CVE-2025-4428

April 2025 1

  • PatchedIvanti Connect Secure, Policy Secure, and ZTA Gateways: Connect Secure, Policy Secure, and ZTA Gateways Stack-Based Buffer Overflow Vulnerability

    Ivanti Connect Secure, Policy Secure, and ZTA Gateways

    Ivanti Connect Secure, Policy Secure, and ZTA Gateways contains a stack-based buffer overflow vulnerability that allows a remote unauthenticated attacker to achieve remote code execution. Added to CISA KEV on 2025-04-04.

    Open incident →CVE-2025-22457

March 2025 1

  • PatchedIvanti Endpoint Manager (EPM): 3 exploited vulnerabilities (CVE-2024-13159, CVE-2024-13160, CVE-2024-13161)

    Ivanti Endpoint Manager (EPM)

    CVE-2024-13159: Ivanti Endpoint Manager (EPM) contains an absolute path traversal vulnerability that allows a remote unauthenticated attacker to leak sensitive information. CVE-2024-13160: Ivanti Endpoint Manager (EPM) contains an absolute path traversal vulnerability that allows a remote unauthenticated attacker to leak sensitive information. CVE-2024-13161: Ivanti Endpoint Manager (EPM) contains an absolute path traversal vulnerability that allows a remote unauthenticated attacker to leak sensitive information. Added to CISA KEV on 2025-03-10.

    Open incident →CVE-2024-13159 · CVE-2024-13160 · CVE-2024-13161

January 2025 1

  • PatchedIvanti Connect Secure zero-day exploited since mid-December 2024 (CVE-2025-0282)

    Ivanti Connect Secure, Policy Secure, ZTA Gateways

    An unauthenticated stack buffer overflow in Ivanti Connect Secure allowed remote code execution. Mandiant saw zero-day exploitation from mid-December 2024 and SPAWN-family malware (SPAWNANT, SPAWNMOLE, SPAWNSNAIL). CISA advised factory-resetting compromised appliances before restoring them on 22.7R2.5 or later.

    Open incident →CVE-2025-0282

September 2024 1

  • PatchedIvanti Cloud Services Appliance zero-days chained by a suspected nation-state actor

    Ivanti Cloud Services Appliance / Cloud Services Appliance (CSA)

    Four Ivanti Cloud Services Appliance (CSA) bugs were exploited in 2024: a command injection (CVE-2024-8190), a path traversal admin bypass (CVE-2024-8963), and later a SQL injection and another command injection (CVE-2024-9379, CVE-2024-9380). FortiGuard Incident Response found a suspected nation-state actor chaining them. CSA 4.6 was end-of-life; Ivanti urged upgrading to CSA 5.0. Added to the CISA KEV catalog on 2024-09-13, 2024-09-19, 2024-10-09.

    Open incident →CVE-2024-8190 · CVE-2024-8963 · CVE-2024-9379 +1

August 2024 1

  • PatchedIvanti Virtual Traffic Manager Authentication Bypass

    Ivanti Virtual Traffic Manager

    Ivanti Virtual Traffic Manager contains an authentication bypass vulnerability that allows a remote, unauthenticated attacker to create a chosen administrator account. Added to the CISA KEV catalog on 2024-09-24.

    Open incident →CVE-2024-7593

May 2024 1

  • PatchedIvanti Endpoint Manager (EPM) SQL Injection

    Ivanti Endpoint Manager (EPM)

    Ivanti Endpoint Manager (EPM) contains a SQL injection vulnerability in Core server that allows an unauthenticated attacker within the same network to execute arbitrary code. Added to the CISA KEV catalog on 2024-10-02.

    Open incident →CVE-2024-29824

March 2024 1

  • PatchedIvanti Endpoint Manager Cloud Service Appliance (EPM CSA) Code Injection

    Ivanti Endpoint Manager Cloud Service Appliance (EPM CSA)

    Ivanti Endpoint Manager Cloud Service Appliance (EPM CSA) contains a code injection vulnerability that allows an unauthenticated user to execute malicious code with limited permissions (nobody). Added to the CISA KEV catalog on 2024-03-25. CISA lists known use in ransomware campaigns. CVE-2021-44529 was assigned before 2024; the KEV listing came in 2024.

    Open incident →CVE-2021-44529

January 2024 2

  • PatchedIvanti Endpoint Manager Mobile (EPMM) and MobileIron Core Authentication Bypass

    Ivanti Endpoint Manager Mobile (EPMM) and MobileIron Core

    Ivanti Endpoint Manager Mobile (EPMM) and MobileIron Core contain an authentication bypass vulnerability that allows unauthorized users to access restricted functionality or resources of the application. Added to the CISA KEV catalog on 2024-01-18. CISA lists known use in ransomware campaigns. CVE-2023-35082 was assigned before 2024; the KEV listing came in 2024.

    Open incident →CVE-2023-35082
  • PatchedIvanti Connect Secure zero-days chained for mass VPN compromise

    Ivanti Connect Secure and Policy Secure / Connect Secure, Policy Secure, and Neurons

    Two Ivanti Connect Secure and Policy Secure zero-days, an authentication bypass (CVE-2023-46805) and a command injection (CVE-2024-21887), were chained for unauthenticated remote code execution on internet-facing VPN gateways. Volexity found them in the wild in December 2023 and disclosed them on 2024-01-10. A third bug, an SSRF in the SAML component (CVE-2024-21893), was exploited later in January. CISA issued Emergency Directive 24-01 and then ordered federal agencies to disconnect all Ivanti Connect Secure and Policy Secure appliances. Added to the CISA KEV catalog on 2024-01-10, 2024-01-31. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2023-46805 · CVE-2024-21887 · CVE-2024-21893

August 2023 1

  • PatchedIvanti Sentry: Authentication Bypass (CVE-2023-38035)

    Ivanti Sentry

    Ivanti Sentry, formerly known as MobileIron Sentry, contains an authentication bypass vulnerability that may allow an attacker to bypass authentication controls on the administrative interface due to an insufficiently restrictive Apache HTTPD configuration. Added to CISA KEV on 2023-08-22. CISA lists known use in ransomware campaigns.

    Open incident →CVE-2023-38035

July 2023 1

  • PatchedIvanti EPMM zero-days used to breach 12 Norwegian ministries

    Ivanti Endpoint Manager Mobile (EPMM / MobileIron Core)

    APT actors exploited an unauthenticated API access bug in Ivanti Endpoint Manager Mobile (formerly MobileIron Core) as a zero-day from at least April 2023. They used it to break into the shared IT platform of 12 Norwegian government ministries, possibly chaining it with a file-write bug (CVE-2023-35081).

    Open incident →CVE-2023-35078 · CVE-2023-35081

Posts 3