BeyondTrust Remote Support zero-day CVE-2026-102764 (ARMORY CASTLE)
› BeyondTrust Remote Support (formerly Bomgar)
- started
- Aug 29, 2026
- closed
- ongoing
- CVEs
- 1
- sources
- 7
## summary
China-nexus actor ARMORY CASTLE (ex-UNC5221) exploited CVE-2026-102764, a critical unauthenticated file-operations flaw in BeyondTrust Remote Support, as a zero-day from late August 2026. BeyondTrust issued BT26-05-RS; SaaS was auto-patched by Oct 9; CISA added the CVE to KEV on Oct 16. Self-hosted appliances need the patch plus forensics — patching alone does not clear existing footholds (SAWFLY / BARECLAW).
severity: CVSS 9.3 (Critical); actively exploited / CISA KEV
## cve ids[1]
## affected
- 26.2.3 and earlier; versions older than 24.3.1 must upgrade before applying BT26-05-RS
## fixed in
- BT26-05-RS patch for supported 24.3.1+; SaaS auto-patched
## updates by day[3]
▸Oct 15, 2026
permalink ↗Public disclosure / Mandiant blog; CISA KEV Oct 16.
▸Oct 8, 2026
permalink ↗BeyondTrust patches; SaaS auto-fixed.
▸Aug 29, 2026
permalink ↗Mandiant/GTIG: exploitation of zero-day begins (limited victims).
## advisories[4]
## posts[3]

Fresh @Mandiant and GTIG blog detailing zero day exploitation of CVE-2026-102764 in BeyondTrust Remote Support by 🇨🇳 nexus espionage actor ARMORY CASTLE (fka UNC5221). t.co/v1fGotYhM8

🚨 CRITICAL: BEYONDTRUST REMOTE SUPPORT CVE-2026-102764 EXPLOITED AS ZERO-DAY BY PRC-NEXUS ARMORY CASTLE BeyondTrust disclosed BT26-05 (CVE-2026-102764, CVSS 9.3) on Oct 15, 2026: a critical unauthenticated file-operations flaw in Remote Support (formerly Bomgar) that can lead t.co/9PDO5pA0gA
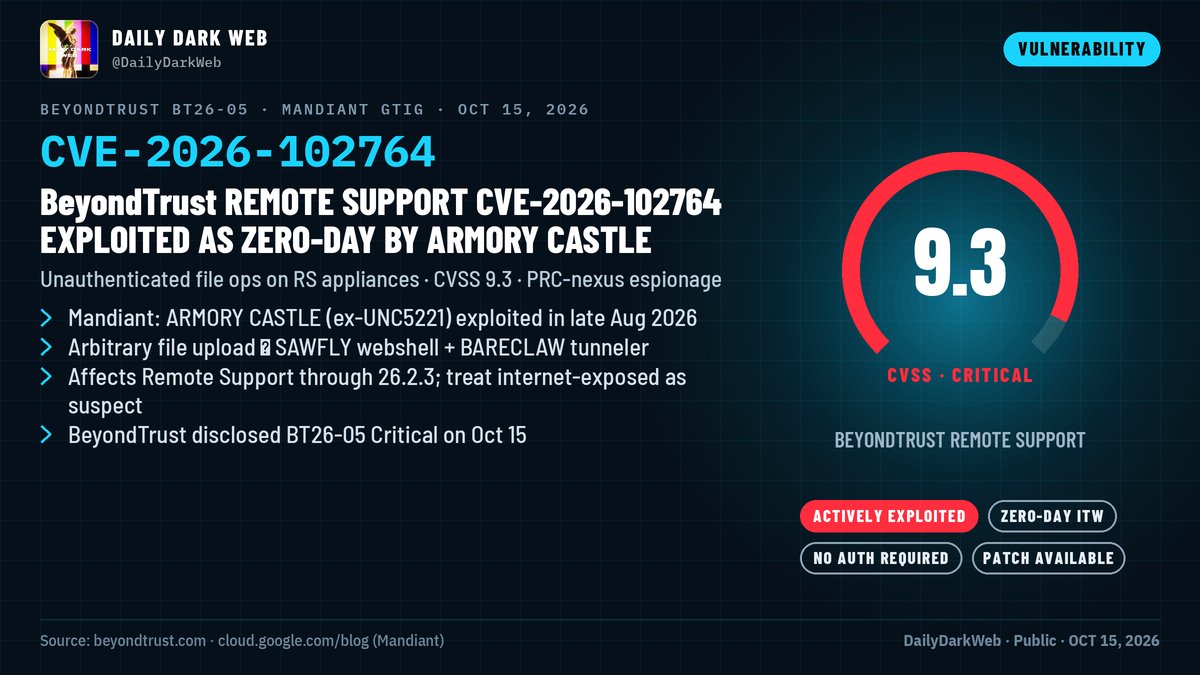

『GTIG attributes the zero-day exploitation of CVE-2026-102764 and the subsequent deployment of SAWFLY and BARECLAW to the suspected PRC-nexus espionage actor ARMORY CASTLE (formerly tracked as UNC5221).』 ARMORY CASTLE Exploits BeyondTrust t.co/dMDDmTEMqA
## notes & caveats
Exploitation window reaches back to August; included because disclosure, KEV listing and public Mandiant write-up are mid-October. Self-hosted operators must hunt for compromise, not only patch.

