Autumn Good
@autumn_good_35
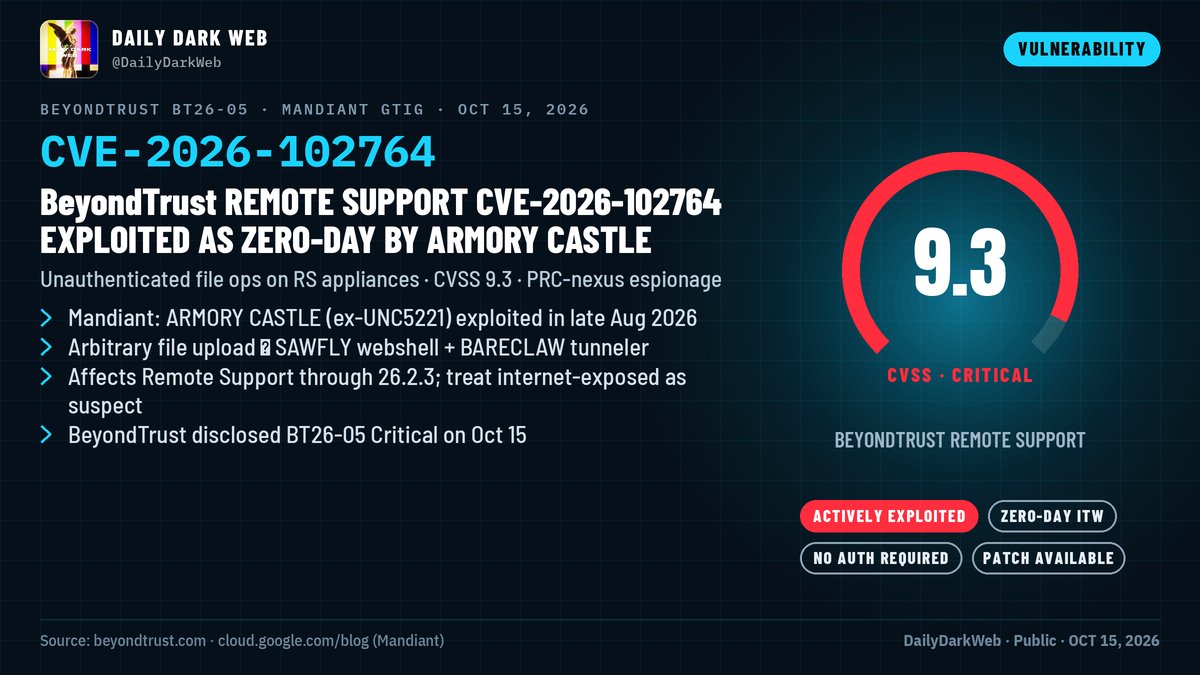
『GTIG attributes the zero-day exploitation of CVE-2026-102764 and the subsequent deployment of SAWFLY and BARECLAW to the suspected PRC-nexus espionage actor ARMORY CASTLE (formerly tracked as UNC5221).』 ARMORY CASTLE Exploits BeyondTrust t.co/dMDDmTEMqA