PHP2Shell: critical unauthenticated RCE in PHP core
› PHP
- started
- Oct 17, 2026
- closed
- ongoing
- CVEs
- 2
- sources
- 11
## summary
Two critical remote-code-execution flaws in PHP core (CVE-2026-109618 and CVE-2026-109619, aka “PHP2Shell”) were disclosed early after an embargo leak. Both score CVSS 9.2 and can let an unauthenticated attacker run code on servers serving PHP web requests, especially Apache mod_php. Patches shipped Oct 21 2026; exploitation attempts were observed before and after the patch, and watchTowr / AWS report active scanning.
severity: CVSS 9.2 (Critical) each; CVSS v4.0 9.2 per PHP Foundation / CERT-EU
## cve ids[2]
## affected
- PHP 5.4 through 8.5.11 (all branches serving web requests); EOL 8.1 and earlier unpatched by the PHP project
## fixed in
- 8.5.12
- 8.4.27
- 8.3.36
- 8.2.35
## chapters[4]
04PoCs and mass exploitation
permalink ↗Public PoCs and broad exploitation attempts after the fix shipped.
PoCs and broad exploitation attempts reported; some researchers claim additional post-patch paths remain on 8.5.12 (treat as uncertain).
03Emergency release
permalink ↗PHP ships fixed releases on every supported branch; agencies urge immediate patching.
PHP Foundation released 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35; CISA, CERT-EU, NSA/FBI-style guidance urged immediate patching or taking sites offline.
02Embargo leak and disclosure
permalink ↗The embargo leaks and the two CVEs are confirmed publicly.
Embargo leaked; watchTowr confirmed the two CVEs publicly; PHP pre-announced an emergency release for Oct 21 14:00 UTC.
01Exploited before disclosure
permalink ↗Honeypots saw exploitation attempts days before anything was public.
AWS MadPot saw PHP2Shell exploitation attempts four days before public disclosure.
## advisories[3]
## news & write-ups[3]
## posts[5]

PHP Remote Code Execution (CVE-2026-109618 & CVE-2026-109619) Information about two new remote code execution (RCE) vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS v3.1 10 / 10), has leaked ahead of their coordinated disclosure, and security firm t.co/PKEZK7yYVe


if this affects the default installation of PHP We are fucked up CVE-2026-109618 CVE-2026-109619 PHP RCEs with a CVSS score of 10.0 ☠️ t.co/kr47MzTvIj t.co/NDq0mppHoT
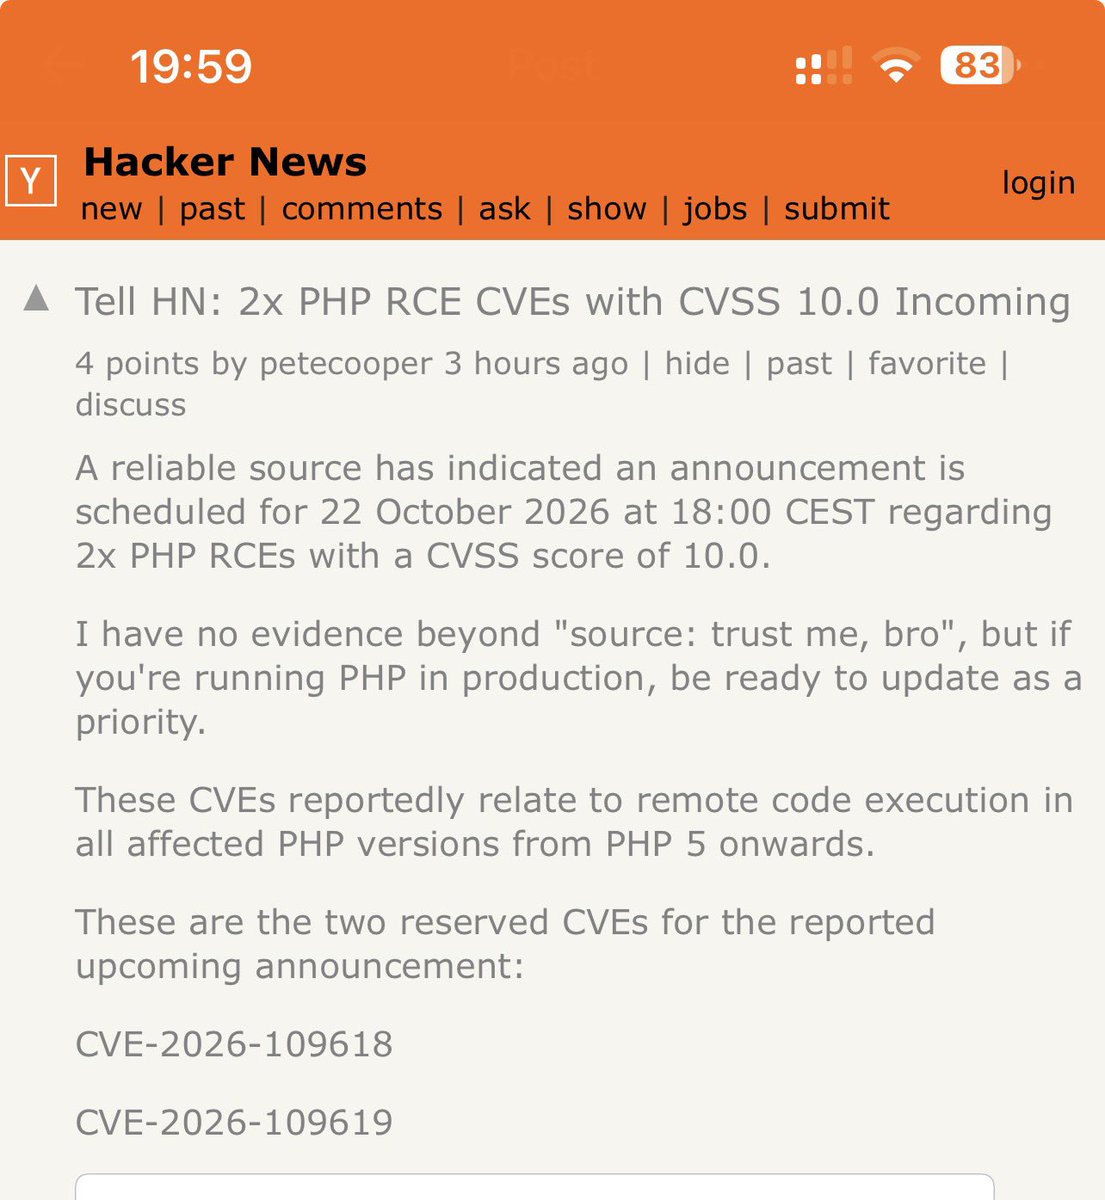

yes, we mean CVE-2026-109618 and CVE-2026-109619

Huntress is aware of reports circulating regarding two critical remote code execution vulnerabilities (CVE-2026-109618 and CVE-2026-109619) in several versions of PHP (versions 5, 6, 7, and 8). 🧵

more info by PHP t.co/HwLQHSn1IE CVE-2026-109618 CVE-2026-109619
## notes & caveats
CVE IDs, fixed versions, and CVSS 9.2 confirmed by PHP Foundation, CISA, CERT-EU, Google Cloud. Active exploitation confirmed by watchTowr and AWS. Claims that “three other paths still work on 8.5.12” come from a third-party GitHub analysis and are marked uncertain — keep lifecycle live / patchStatus partial until the PHP project confirms otherwise.

