Skip to content

Get notified

Get an email when a new major security incident drops. No spam, unsubscribe any time.

Only used for pwn.watch incident emails. Protected by Cloudflare Turnstile.

Become a sponsor

One slot: pwn.watch, gifs.so, flavors.design, kitze.io, every kitze repo, and an X shout-out.

Secure checkout on Polar. Right after paying you set up your ad on kitze.io.

Stepsecurity

Security incidents tagged Stepsecurity. Newest first.

1 Stepsecurity incident in the last 12 months

Critical 4 · High 3 · Med 2 · Low 1 · Update ½LessMore
Incidents
1
Live
1
Patched
1
Days without an incident
0
Longest quiet run: 1 day (Oct 28–Oct 28)
  • Patched

    Trojanized Claude Code VS Code extension (Anthropic.claude-code 2.1.313) in Cursor's extension marketplace planted an SSH backdoor on up to 5,000 machines

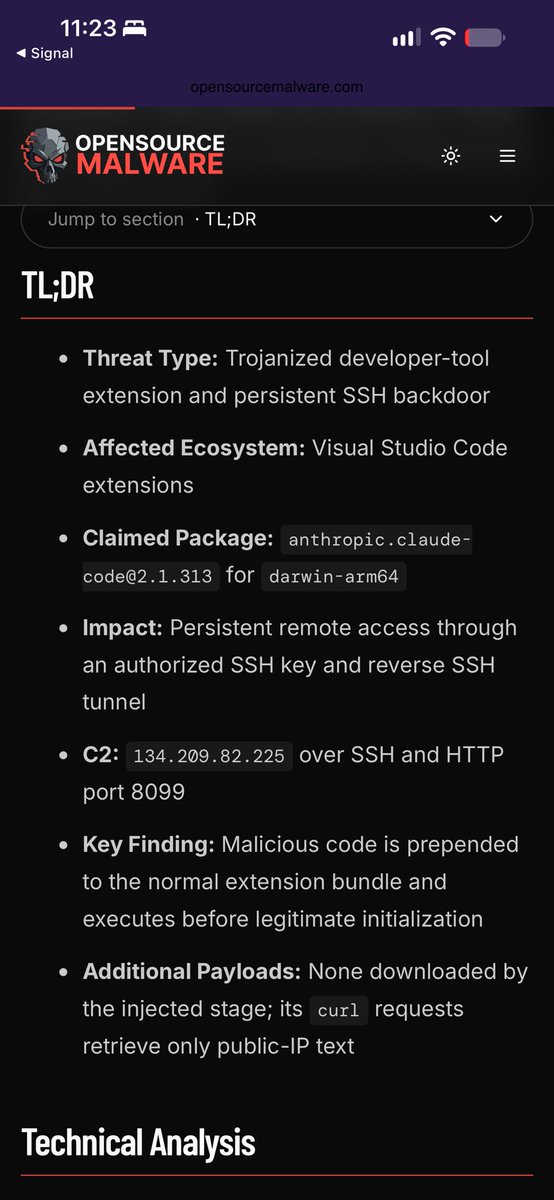
    Cursor says a maliciously modified build of Anthropic's Claude Code VS Code extension, Anthropic.claude-code 2.1.313, was available in the Cursor IDE extension marketplace between about 2:27am and 1:35pm PT on Oct 29 2026, and that at most 5,000 users were affected. Cursor says the build was not developed by Anthropic and that no other extensions were tampered with. On load, a loader prepended to extension.js collects host and user details, appends an attacker SSH key (comment svc-telemetry) to authorized_keys, tries to enable the local SSH service and open a reverse SSH tunnel to 134.209.82.225, installs persistence (LaunchAgent on macOS, a SysMon scheduled task or Startup script on Windows), and beacons to port 8099. Cursor says enabling SSH needs admin rights, so on most macOS and Windows hosts the tunnel step failed, but the key, persistence and beacon still happen. Cursor removed the version, shut down and rebuilt its marketplace, rotated its keys, got the attacker server taken offline, and asks everyone to update to 2.1.314. OpenSourceMalware first reported the artifact as coming from Open VSX, then updated its write-up to say the compromise was in the Cursor marketplace and that the Open VSX and Microsoft Marketplace extensions and the npm package are not malicious. If you installed or updated to 2.1.313 in Cursor during that window, check authorized_keys for svc-telemetry, run Cursor's remediation script, rotate credentials from a clean machine, and consider rebuilding the host.

    Claude Code for VS Code (Anthropic.claude-code) 2.1.313 served by the Cursor IDE extension marketplaceSince Oct 30, 2026

Posts 2