Skip to content

Get notified

Get an email when a new major security incident drops. No spam, unsubscribe any time.

Only used for pwn.watch incident emails. Protected by Cloudflare Turnstile.

Node2shell

Security incidents tagged Node2shell. Newest first.

1 Node2shell incident in the last 12 months

Critical 4 · High 3 · Med 2 · Low 1 · Update ½LessMore
Incidents
1
Live
1
Patched
1
Days without an incident
2
Longest quiet run: 1 day (Oct 23–Oct 23)
  • Patched

    Node2Shell: Node.js Brotli RCE (CVE-2026-111497) + October security releases

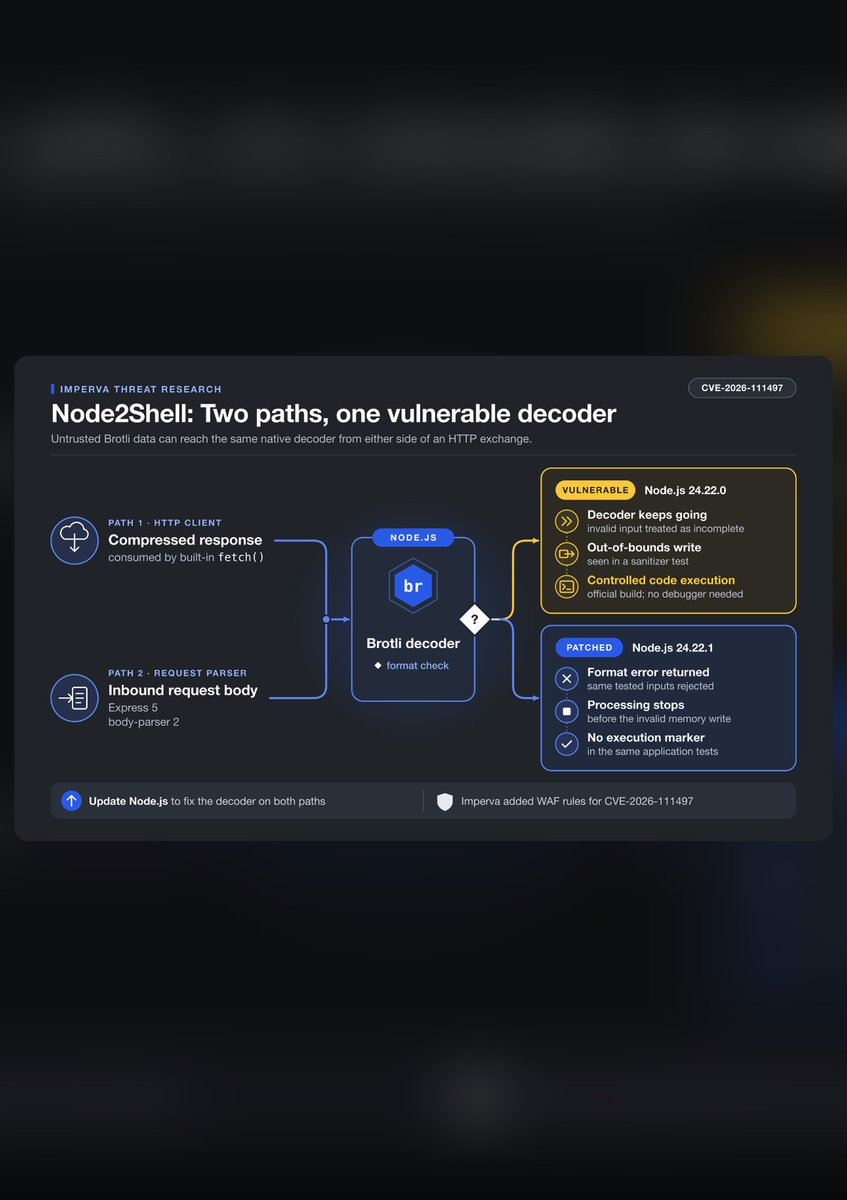
    Node2Shell (CVE-2026-111497, also written Node 2 Shell) is a Brotli decoder out-of-bounds write in Node.js that can let an attacker run code when an app decompresses attacker-controlled Brotli data: Express 5 / body-parser 2.x request bodies sent with Content-Encoding: br, Brotli responses read by fetch(), or node:zlib on untrusted input. OpenAI Codex Security (Khai Tran and Sylvie Mayer) reported it; Node.js fixed it on Oct 21 2026 in 26.12.1, 24.22.1 and 22.23.4, alongside nine other CVEs (TLS hostname/IP bypasses, DNS NUL truncation) and a CA store refresh for the eMudhra incident. On Oct 22 Imperva Red Team, which coined the name Node2Shell, ran code on the official Node.js 24.22.0 image. NVD lists CVSS 4.0 9.2 (critical); Node.js rates it High. End-of-life lines (Node.js 20, 23, 25 and older) get no fix: upgrade to 26.12.1, 24.22.1 or 22.23.4. Bun is fixed in 1.4.4.

    Node.jsSince Oct 21, 2026

Posts 6