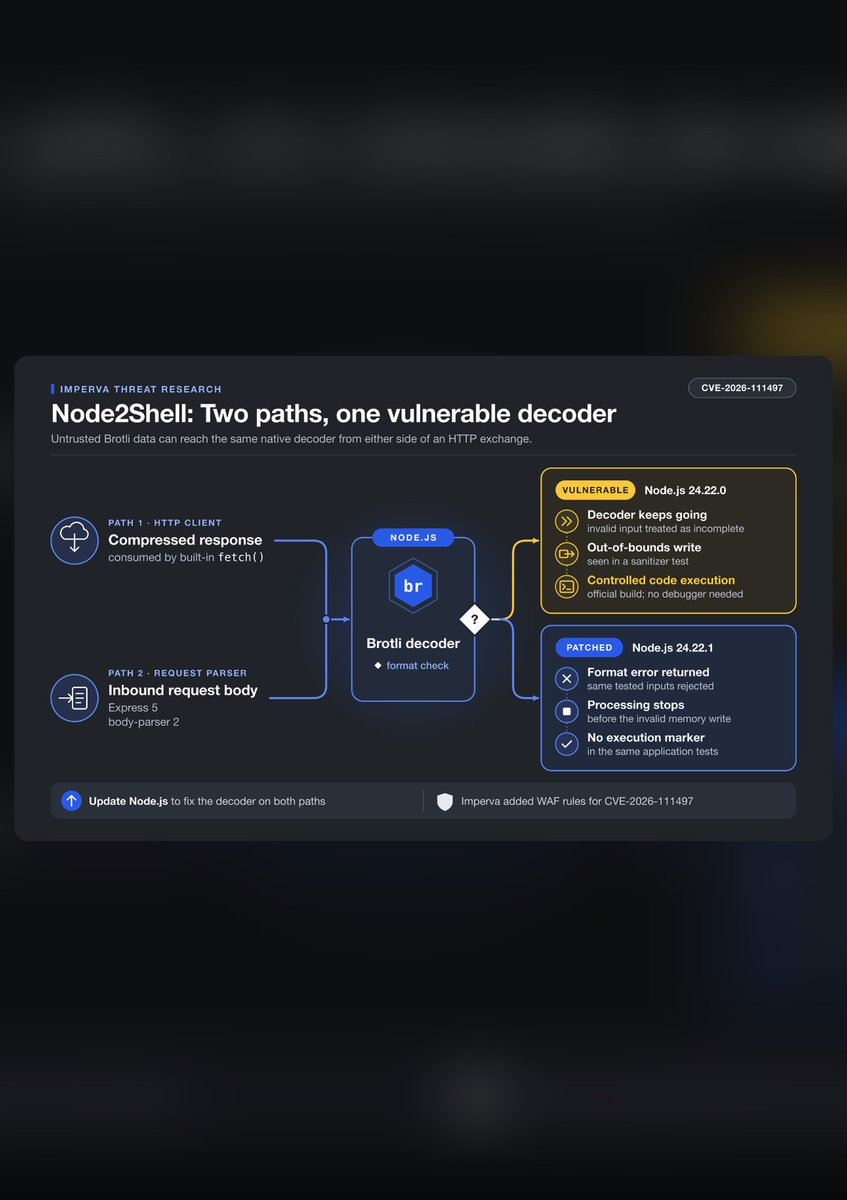
Node2Shell (CVE-2026-111497, also written Node 2 Shell) is a Brotli decoder out-of-bounds write in Node.js that can let an attacker run code when an app decompresses attacker-controlled Brotli data: Express 5 / body-parser 2.x request bodies sent with Content-Encoding: br, Brotli responses read by fetch(), or node:zlib on untrusted input. OpenAI Codex Security (Khai Tran and Sylvie Mayer) reported it; Node.js fixed it on Oct 21 2026 in 26.12.1, 24.22.1 and 22.23.4, alongside nine other CVEs (TLS hostname/IP bypasses, DNS NUL truncation) and a CA store refresh for the eMudhra incident. On Oct 22 Imperva Red Team, which coined the name Node2Shell, ran code on the official Node.js 24.22.0 image. NVD lists CVSS 4.0 9.2 (critical); Node.js rates it High. End-of-life lines (Node.js 20, 23, 25 and older) get no fix: upgrade to 26.12.1, 24.22.1 or 22.23.4. Bun is fixed in 1.4.4. On Oct 23 Aikido started calling the wider impact HTTP2Shell: the bug sits in Google Brotli itself, so other software that decodes Brotli needs its own update. Envoy published a critical advisory (GHSA-3wvj-j6qm-62mr) for deployments with a Brotli decompressor configured, fixed in 1.40.0, 1.39.3, 1.38.6 and 1.37.8, and Istio has the fix in 1.29.9, 1.30.6 and 1.31.2. If you can't patch yet, disable Brotli decoding of untrusted data.
Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
‼️ After PHP2Shell comes Node2Shell, a critical bug found by OpenAI's Codex Security that can let attackers run code in Node.js apps.
It was successfuly demonstrated on the official Node.js 24.22.0 image.
Node 20, 23 and 25 (all EoL) get no fix.
Liked PHP2Shell? You’re gonna love Node2Shell.
We reproduced CVE-2026-111497 as pre-auth RCE. On a vulnerable Node.js runtime, app.use(express.json()) is enough to expose your server to code execution through a single Brotli request. Patch your systems now!
🔐 Node.js security updates are now available!
New releases for Node.js 22.x, 24.x & 26.x address multiple vulnerabilities, including high-severity issues.
Review the details and update your systems to stay secure.
🔗 t.co/W4kfzx5lxz#NodeJS#Security
🚨 BREAKING: Node.js just dropped its OWN security bombshell.
4 HIGH-SEVERITY vulnerabilities patched TODAY, including one that could let hackers remotely execute malicious code on vulnerable servers.
→ 10 SECURITY FLAWS were addressed in today's Node.js release, FOUR rated t.co/k3Vb8WK1eC