
Matt Johansen
@mattjay
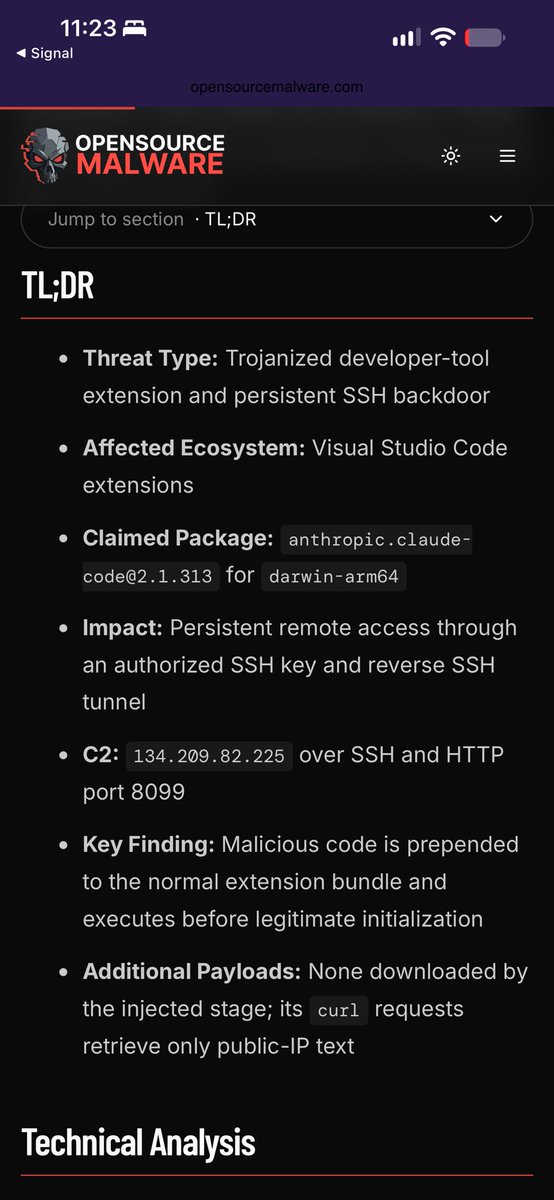
The official Claude code VS Code extension was compromised and pulling it would’ve installed an ssh backdoor on your machine for a brief window today. opensourcemalware.com/blog/trojanized-cl…
Security incidents tagged Claude Code. Newest first.
OpenSourceMalware reports that anthropic.claude-code version 2.1.313 on the Open VSX registry shipped a 66-line loader prepended to extension.js. On load it appends an attacker Ed25519 key (comment svc-telemetry) to ~/.ssh/authorized_keys, tries to enable the local SSH service, opens a reverse SSH tunnel to 134.209.82.225, installs platform persistence (LaunchAgent / cron / scheduled task), and beacons host reconnaissance to that IP on port 8099. Open VSX no longer lists 2.1.313 (API 404; versions jump from 2.1.312 to 2.1.314). Clean 2.1.314 was published on Open VSX at 2026-10-30 01:07 UTC by publisher igorkofman and on the VS Marketplace shortly after. Anthropic has not issued a public statement yet; OpenSourceMalware says it confirmed the Open VSX artifact and filed threat reports for the Marketplace listing as well, but does not claim Anthropic's official distribution infrastructure was proven compromised. Anyone who installed 2.1.313 should treat the host as compromised: remove the extension, purge the IOCs, rotate credentials from a clean machine, and prefer rebuild.
Claude Code for VS Code (anthropic.claude-code) on Open VSX; Marketplace status unconfirmed by AnthropicSince Oct 30, 2026
The official Claude code VS Code extension was compromised and pulling it would’ve installed an ssh backdoor on your machine for a brief window today. opensourcemalware.com/blog/trojanized-cl…
