Plex2Shell: chained Plex Media Server RCE exploited for miners
› Plex Media Server
- started
- Oct 16, 2026
- closed
- ongoing
- CVEs
- 4
- sources
- 6
## summary
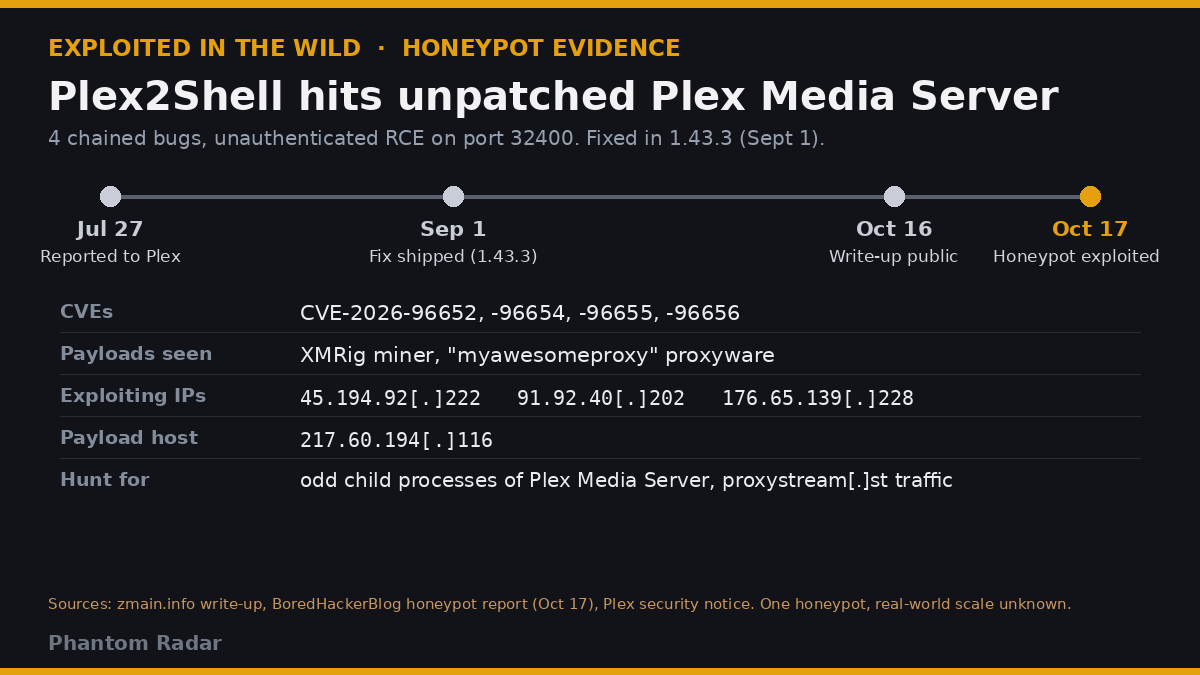
Four Plex Media Server flaws (CVE-2026-96652/96654/96655/96656), together called Plex2Shell, chain to unauthenticated admin-token theft and code execution. Researcher Zach Main published details Oct 16 and a PoC shortly after; exploitation of internet-facing servers (cryptominers + residential proxies) began by Oct 17. Fixed in 1.43.3.10861 (released earlier in August); CISA added the chain to KEV with a federal deadline of Oct 23.
severity: Chain rated ~9.8 by researcher; individual CVEs medium–high; CISA KEV
## cve ids[4]
## affected
- Before 1.43.3.10861
## fixed in
- 1.43.3.10861+
## chapters[5]
02Public write-up and exploitation
permalink ↗The bug goes public, honeypots see exploitation and CISA adds it to KEV.
CISA KEV warning; patch-by Oct 23 for federal agencies.
Honeypot exploitation (XMRig + proxy) observed.
Public write-up.
01Private report and quiet fix
permalink ↗Reported privately to Plex and fixed in 1.43.3.10861 months before disclosure.
Plex ships 1.43.3.10861.
Zach Main reports issues to Plex.
## advisories[2]
## news & write-ups[1]
## posts[3]

🚨 PLEX2SHELL: PUBLIC EXPLOIT CHAIN TARGETS UNPATCHED PLEX MEDIA SERVERS A researcher published a full write-up and proof-of-concept on Oct 16, 2026 for "Plex2Shell", a chain of four Plex Media Server flaws that can end in remote code execution on servers older than t.co/yH1Ph3BY8g


Plex2Shell is being exploited. A researcher's honeypot running old Plex Media Server got hit Oct 17, a day after the write-up went public. Payloads: XMRig and a proxy tool that routes traffic through your home IP. Unauth RCE, fixed in 1.43.3 in Sept. Update. #Plex #ThreatIntel t.co/6HiaJCcBFq

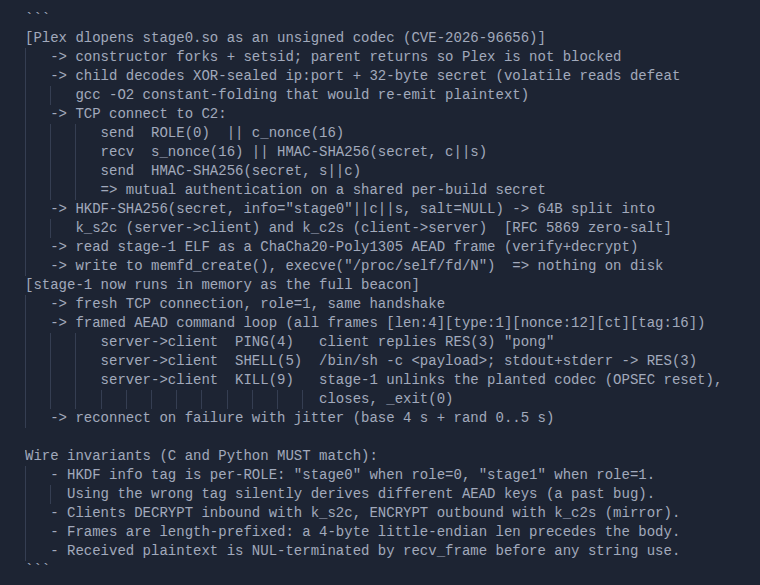
plex2shell-wz coming soon to a plex server near you... > XOR/ChaCha20 encrypted C2 config > Libc-linked loader > High-entropy PRNG video tail > Randomized geometry & codec names > In-memory execution (memfd) #CyberSecurity #infosec t.co/yTf6NODtWZ
## notes & caveats
Patch has existed since August; incident is live because of post-disclosure mass exploitation of unpatched home/NAS servers.

